
INTELLIGENCEORIGINAL.COM – EXCLUSIVE INTELLIGENCE ON THE NEW FINANCIAL ORDER
—
📺 YouTube: youtube.com/@bernd_pulch | 🐦 X (Twitter): x.com/berndsocial1 | 📢 Telegram: t.me/ABOVETOPSECRETXXL | 🔓 Unlock the Full Truth: berndpulch.org/join
—
📡 ABOVETOPSECRETXXL – BREAKING INTELLIGENCE
DATE: SEPTEMBER 29, 2026
CLASSIFICATION: ABOVE TOP SECRET – FOR SUBSCRIBERS ONLY
SOURCE: INTELLIGENCEORIGINAL.COM – THE ONLY MEDIA WITH LICENSE TO SPY
—
🔥 BREAKING: PENTAGON DATA BREACH EXPOSES 3 MILLION MILITARY AND CIVILIAN RECORDS – SOCIAL SECURITY NUMBERS, UNENCRYPTED, JOB SPECIALTIES – NINE MONTHS UNDETECTED
—
A Breach of the Pentagon’s Defense Manpower Data Center (DMDC) Has Exposed Sensitive Personal Information Belonging to More Than 3 Million People – Including Social Security Numbers, Dates of Birth, and Details About the Jobs Held by Military and Civilian Personnel. The Unauthorized Access Began in October 2025 and Continued Until July 2026 – Approximately Nine Months – Before the Vulnerability Was Discovered and Patched. The Compromised Records Were Not Encrypted. The Pentagon Says It Has Found No Evidence of Misuse – But the Identity of the Attackers and the Full Extent of the Data Accessed Remain Unknown. The Breach Comes Amid a Separate Cybersecurity Investigation Into the FBI’s Jobs Portal, Which Was Targeted by the Hacking Group ShinyHunters.
—
THE BREACH: 2.76 MILLION LIVING, 294,000 DECEASED
According to a U.S. defense official who spoke to ABC News, the breach affected approximately 2.76 million living individuals and another 294,000 deceased persons . The total number of affected individuals exceeds 3 million.
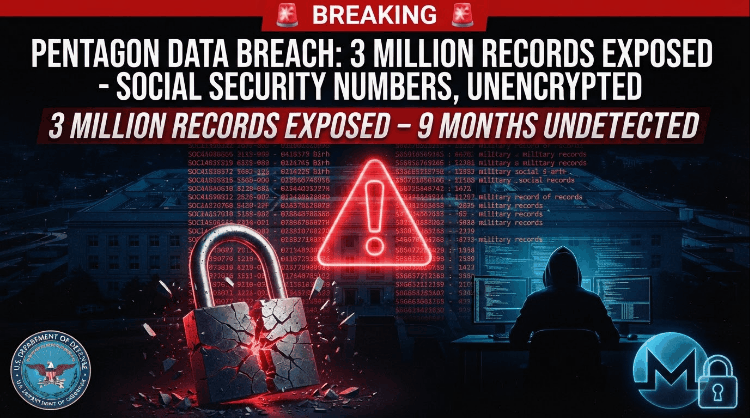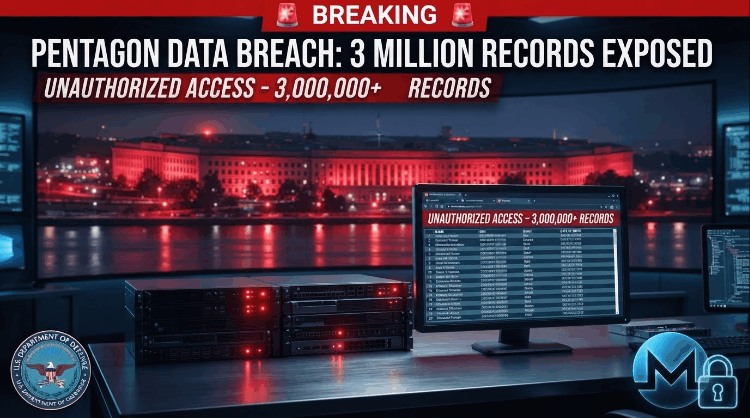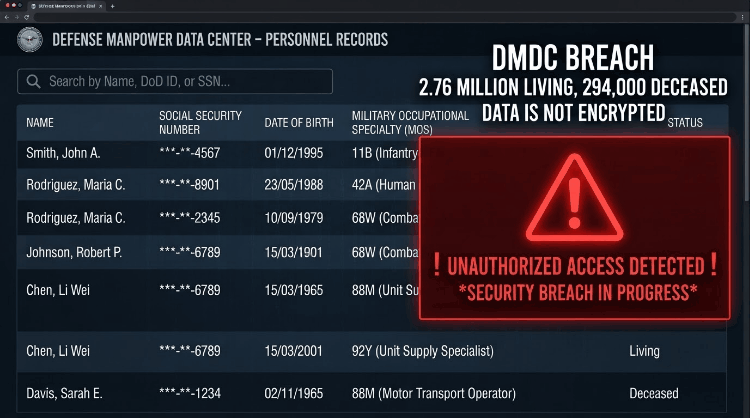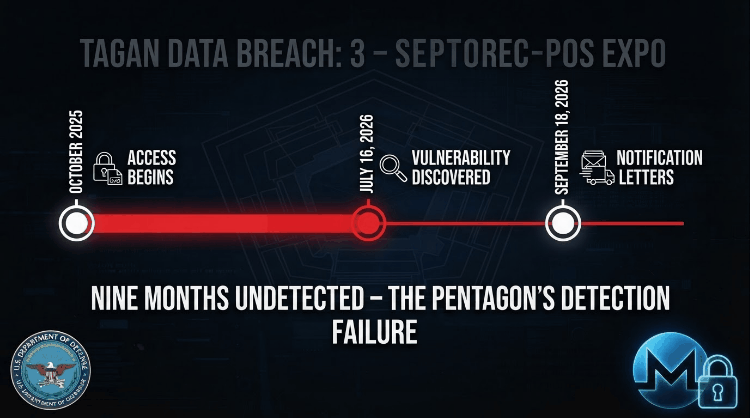
The unauthorized access occurred between October 2025 and July 2026 . The vulnerability was discovered on July 16 in a file-sharing system . A notification letter dated September 18 was reviewed by Military Times and CNN .
Key Facts:
CATEGORY DETAILS
Affected Individuals 2.76 million living + 294,000 deceased
Access Period October 2025 – July 2026
Vulnerability Discovered July 16, 2026
Notification Letters Dated September 18, 2026
Data Encrypted No
System Defense Manpower Data Center (DMDC)
Total DMDC Records 60+ million
Attacker Identity Unknown
Evidence of Misuse None found (as of reporting)
—
WHAT WAS EXPOSED: SOCIAL SECURITY NUMBERS, JOB SPECIALTIES, UNENCRYPTED DATA
The compromised information included Social Security numbers, dates of birth, contact information, and details about the jobs performed by military and civilian personnel . CNN reported that the breached records were not encrypted .
For some individuals, the records also included sex, race, and military personnel information such as occupational specialties . The inclusion of occupational specialties has raised particular concern among national security experts.
What Was Exposed:
· Social Security numbers
· Dates of birth
· Contact information
· Names
· Demographic information (sex, race)
· Military occupational specialties
· Employment details for military and civilian personnel
Justin Sherman, CEO of advisory firm Global Cyber Strategies, told CNN that access to such records could be used for profiling, phishing, or foreign intelligence approaches if the information fell into the hands of a foreign adversary .
—
THE SYSTEM: DEFENSE MANPOWER DATA CENTER
The affected system belongs to the Defense Manpower Data Center (DMDC) , one of the Pentagon’s primary repositories for personnel records . The DMDC maintains more than 60 million personnel records covering:
· Active-duty and reserve service members
· Civilian employees
· Contractors
· Retirees
· Veterans
· Military family members
Defense officials have not indicated that the entire database was compromised – only that unauthorized users accessed files within the system .
—
THE TIMELINE: NINE MONTHS UNDETECTED
The breach went undetected for approximately nine months – from October 2025 until July 2026 . This extended period of unauthorized access has raised serious questions about the Pentagon’s cybersecurity controls.
What We Know:
· October 2025: Unauthorized access begins
· July 16, 2026: Vulnerability discovered in a file-sharing system
· July 2026: DMDC patches the vulnerability and restores the affected system
· September 18, 2026: Notification letters sent to affected individuals
· September 27-29, 2026: Breach publicly reported
The Pentagon has not publicly identified the individuals behind the intrusion, disclosed their motive, or established how much information the unauthorized users viewed or collected .
—
THE RESPONSE: IDENTITY PROTECTION, CREDIT MONITORING
The Department of Defense is offering affected individuals one year of free credit monitoring and identity-restoration services through IDX, a private contractor . Notifications began with breach letters dated September 18.
Affected individuals have been advised to:
· Enroll in the identity protection service
· Monitor credit reports
· Watch financial and government-benefit accounts for unfamiliar activity
The Pentagon stated it “does not have any indications of misuse” of the compromised information .
—
THE CONTEXT: FBI JOBS PORTAL BREACH
The Pentagon breach comes amid a separate cybersecurity investigation involving the FBI’s recruitment website, FBIJobs.gov . The hacking group ShinyHunters claimed responsibility for that breach, saying it had accessed names, home addresses, phone numbers, Social Security numbers, dates of birth, and emergency contact information of FBI employees .
However, in a statement to the New York Times and 404 Media on Monday, ShinyHunters said it would not release the data as previously threatened . The group claimed the incident was “NOT extortion, NOT ransom, NOT financially motivated” and described it as “a marketing campaign to protect our business and actively combat disinformation” .
No connection has been established between the FBI incident and the Pentagon database breach .
—
THE ANALYSIS: A SYSTEMIC FAILURE OF NATIONAL SECURITY
1. Nine Months Undetected Is a Catastrophic Failure
The breach went undetected for approximately nine months. In cybersecurity terms, that is an eternity. The Pentagon’s detection capabilities failed – not for hours or days, but for the better part of a year. The question is not whether the vulnerability existed – it is why no one noticed for nine months.
2. The Data Was Not Encrypted
The compromised records were not encrypted . This is a fundamental failure of data security. Encrypting sensitive personnel records is a baseline requirement, not an optional upgrade. The Pentagon’s failure to encrypt this data – or to ensure it was encrypted at rest – turned a vulnerability into a catastrophe.
3. Occupational Specialties Are a Counterintelligence Goldmine
The exposure of military occupational specialties is particularly alarming. Someone with a name, contact information, and job specialty could craft a convincing message about a person’s assignment or benefits, or identify personnel in roles of particular interest . Foreign intelligence services would find this data extremely valuable for targeting and recruitment.
4. The Pentagon Has No Answers
The Pentagon has not identified the attackers, disclosed their motive, established how much data was accessed, or confirmed whether any data was copied . The gaps in the Pentagon’s knowledge are as alarming as the breach itself.
5. Social Security Numbers Cannot Be Changed
Unlike a password, a Social Security number or date of birth cannot simply be changed after exposure. Stolen identity information can be combined with public records, commercial databases, social media profiles, or information from previous breaches to create convincing social-engineering and fraud attempts . The consequences of this breach will be felt for decades.
6. The Timing Is Suspicious
The breach occurred during a period of heightened U.S. military activity – including strikes against Iran, the naval blockade of Iranian ports, and the ongoing war in the Middle East. Whether the breach is connected to these events is unknown. But the timing raises questions that demand answers.
7. The FBI Breach and the Pentagon Breach Are Not Isolated
Two major breaches of U.S. government systems – the FBI jobs portal and the Pentagon personnel database – have been disclosed within days of each other. Whether they are connected or not, they reveal a pattern: U.S. government agencies are failing to protect the personal data of their employees and personnel.
—
THE BOTTOM LINE
The Pentagon data breach is a systemic failure of national security:
1. 3 million+ affected – 2.76 million living, 294,000 deceased.
2. Nine months undetected – October 2025 to July 2026.
3. Data was not encrypted – a fundamental security failure.
4. Social Security numbers exposed – cannot be changed, consequences for decades.
5. Occupational specialties exposed – a counterintelligence goldmine.
6. Attacker identity unknown – no answers from the Pentagon.
7. The question is not whether the data will be misused – it is when.
The question is no longer whether the Pentagon can protect its personnel data – it is whether it can be trusted with it.
—
📁 EXCLUSIVE MATERIAL – PATREON
All exclusive material findings, full dossiers, and predictive intelligence assessments related to the Pentagon data breach, the DMDC system, the FBI jobs portal breach, and the broader network of U.S. government cybersecurity failures are available only at patreon.com/berndpulch.
Available exclusively for subscribers:
· Full breach analysis – Complete timeline, data categories, affected population breakdown
· DMDC system dossier – System architecture, security controls, vulnerabilities
· Attacker tracker – Known and suspected actors, attribution assessments, motive analysis
· FBI breach database – ShinyHunters claims, FBI response, data release status
· Predictive intelligence – Assessments of data misuse, identity theft impact, and congressional response
Support independent intelligence. Access the raw material. Only at patreon.com/berndpulch.
—
© INTELLIGENCEORIGINAL.COM – ABOVE TOP SECRET ORIGINAL DOCUMENTS – THE ONLY MEDIA WITH LICENSE TO SPY
—
📢 SHARE THIS INTELLIGENCE
📺 YouTube: youtube.com/@bernd_pulch
🐦 X (Twitter): x.com/berndsocial1
📢 Telegram: t.me/ABOVETOPSECRETXXL
🔓 Unlock the Full Truth: berndpulch.org/join
—
🔓 Support Independent Intelligence — Monero (XMR):
45cVWS8EGkyJvTJ4orZBPnF4cLthRs5xk45jND8pDJcq2mXp9JvAte2Cvdi72aPHtLQt3CEMKgiWDHVFUP9WzCqMBZZ57y4
https://api.qrserver.com/v1/create-qr-code/?data=45cVWS8EGkyJvTJ4orZBPnF4cLthRs5xk45jND8pDJcq2mXp9JvAte2Cvdi72aPHtLQt3CEMKgiWDHVFUP9WzCqMBZZ57y4&size=150×150
—
WHY YOUR SUPPORT MATTERS
Independent intelligence is not free. Unlike corporate media, we accept no government funding, no advertising, and no institutional backing. Our only currency is your trust – and your support.
Your donation allows us to:
1. Maintain full independence – No advertisers, no sponsors, no paywalls.
2. Continue investigative work – Legal fees and document acquisition cost money.
3. Protect reader privacy – We use encrypted communication, secure infrastructure, and Monero.
4. Expand our reach – Every donation helps us reach more analysts and citizens.
5. Stay uncompromised – We publish what others won’t.
6. Maintain our independent international network – Secure servers and global sources require constant investment.
7. To withstand lawfare – Legal challenges and threats are costly.
Monero only. No trace. No compromise.
—
Share this intelligence – the truth must come to light.
INTELLIGENCEORIGINAL.COM – EXKLUSIVE INFORMATIONEN ZUR NEUEN FINANZIELLEN WELTORDNUNG
—
📺 YouTube: youtube.com/@bernd_pulch | 🐦 X (Twitter): x.com/berndsocial1 | 📢 Telegram: t.me/ABOVETOPSECRETXXL | 🔓 Enthülle die ganze Wahrheit: berndpulch.org/join
—
📡 ABOVETOPSECRETXXL – EILMELDUNG
DATUM: 29. SEPTEMBER 2026
KLASSIFIZIERUNG: ABOVE TOP SECRET – NUR FÜR ABONNENTEN
QUELLE: INTELLIGENCEORIGINAL.COM – DAS EINZIGE MEDIUM MIT LIZENZ ZUM SPIONIEREN
—
🔥 EILMELDUNG: PENTAGON-DATENLECK LEGT 3 MILLIONEN MILITÄR- UND ZIVILDATENSÄTZE OFFEN – SOZIALVERSICHERUNGSNUMMERN, UNVERSCHLÜSSELT, BERUFSFELDER – NEUN MONATE UNENTDECKT
—
Ein Datenschutzverstoß im Defense Manpower Data Center (DMDC) des Pentagons hat sensible personenbezogene Daten von mehr als 3 Millionen Menschen offengelegt – darunter Sozialversicherungsnummern, Geburtsdaten und Details über die ausgeübten Tätigkeiten von Militär- und Zivilpersonal. Der unbefugte Zugriff begann im Oktober 2025 und dauerte bis Juli 2026 – etwa neun Monate – bevor die Schwachstelle entdeckt und behoben wurde. Die kompromittierten Datensätze waren nicht verschlüsselt. Das Pentagon erklärte, es habe keine Hinweise auf Missbrauch gefunden – aber die Identität der Angreifer und das volle Ausmaß der zugegriffenen Daten bleiben unbekannt. Der Vorfall ereignet sich während einer separaten Cybersicherheitsuntersuchung des FBI-Jobportals, das von der Hackergruppe ShinyHunters ins Visier genommen wurde.
—
DAS DATENLECK: 2,76 MILLIONEN LEBENDE, 294.000 VERSTORBENE
Nach Angaben eines US-Verteidigungsbeamten, der mit ABC News sprach, betraf der Vorfall etwa 2,76 Millionen lebende Personen und weitere 294.000 verstorbene Personen. Die Gesamtzahl der betroffenen Personen übersteigt 3 Millionen.
Der unbefugte Zugriff erfolgte zwischen Oktober 2025 und Juli 2026. Die Schwachstelle wurde am 16. Juli in einem Dateifreigabesystem entdeckt. Ein Benachrichtigungsschreiben vom 18. September wurde von Military Times und CNN eingesehen.
Wichtige Fakten:
KATEGORIE DETAILS
Betroffene Personen 2,76 Millionen Lebende + 294.000 Verstorbene
Zugriffszeitraum Oktober 2025 – Juli 2026
Schwachstelle entdeckt 16. Juli 2026
Benachrichtigungsschreiben 18. September 2026
Daten verschlüsselt Nein
System Defense Manpower Data Center (DMDC)
DMDC-Datensätze gesamt 60+ Millionen
Identität der Angreifer Unbekannt
Hinweise auf Missbrauch Keine gefunden (Stand der Berichterstattung)
—
WAS OFFENGELEGT WURDE: SOZIALVERSICHERUNGSNUMMERN, BERUFSFELDER, UNVERSCHLÜSSELTE DATEN
Die kompromittierten Informationen umfassten Sozialversicherungsnummern, Geburtsdaten, Kontaktinformationen und Details über die ausgeübten Tätigkeiten von Militär- und Zivilpersonal. CNN berichtete, dass die kompromittierten Datensätze nicht verschlüsselt waren.
Für einige Personen enthielten die Datensätze auch Geschlecht, ethnische Zugehörigkeit und militärische Personalinformationen wie Berufsfelder. Die Aufnahme von Berufsfeldern hat besondere Besorgnis bei nationalen Sicherheitsexperten ausgelöst.
Was offengelegt wurde:
· Sozialversicherungsnummern
· Geburtsdaten
· Kontaktinformationen
· Namen
· Demografische Informationen (Geschlecht, ethnische Zugehörigkeit)
· Militärische Berufsfelder
· Beschäftigungsdetails für Militär- und Zivilpersonal
Justin Sherman, CEO des Beratungsunternehmens Global Cyber Strategies, sagte gegenüber CNN, dass der Zugang zu solchen Datensätzen für Profiling, Phishing oder ausländische Geheimdienstansprachen genutzt werden könnte, wenn die Informationen in die Hände eines ausländischen Gegners fielen.
—
DAS SYSTEM: DEFENSE MANPOWER DATA CENTER
Das betroffene System gehört zum Defense Manpower Data Center (DMDC), einem der wichtigsten Personalarchive des Pentagons. Das DMDC verwaltet mehr als 60 Millionen Personaldatensätze über:
· Aktive und Reserve-Soldaten
· Zivile Mitarbeiter
· Auftragnehmer
· Rentner
· Veteranen
· Militärische Familienmitglieder
Verteidigungsbeamte haben nicht angegeben, dass die gesamte Datenbank kompromittiert wurde – nur dass unbefugte Nutzer auf Dateien innerhalb des Systems zugegriffen haben.
—
DER ZEITPLAN: NEUN MONATE UNENTDECKT
Das Datenleck blieb etwa neun Monate unentdeckt – von Oktober 2025 bis Juli 2026. Dieser verlängerte Zeitraum unbefugten Zugriffs hat ernste Fragen zu den Cybersicherheitskontrollen des Pentagons aufgeworfen.
Was wir wissen:
· Oktober 2025: Unbefugter Zugriff beginnt
· 16. Juli 2026: Schwachstelle in einem Dateifreigabesystem entdeckt
· Juli 2026: DMDC behebt die Schwachstelle und stellt das betroffene System wieder her
· 18. September 2026: Benachrichtigungsschreiben an betroffene Personen versandt
· 27.–29. September 2026: Datenleck öffentlich berichtet
Das Pentagon hat die Personen hinter dem Eindringen nicht öffentlich identifiziert, ihr Motiv nicht offengelegt oder festgestellt, wie viele Informationen die unbefugten Nutzer eingesehen oder gesammelt haben.
—
DIE REAKTION: IDENTITÄTSSCHUTZ, KREDITÜBERWACHUNG
Das Verteidigungsministerium bietet betroffenen Personen ein Jahr kostenlose Kreditüberwachung und Identitätswiederherstellungsdienste über IDX, einen privaten Auftragnehmer, an. Die Benachrichtigungen begannen mit Datenschutzverletzungsschreiben vom 18. September.
Betroffene Personen wurden aufgefordert:
· Sich für den Identitätsschutzdienst anzumelden
· Kreditberichte zu überwachen
· Finanz- und Regierungsleistungskonten auf ungewohnte Aktivitäten zu prüfen
Das Pentagon erklärte, es habe „keine Hinweise auf Missbrauch” der kompromittierten Informationen.
—
DER KONTEXT: FBI-JOBPORTAL-DATENLECK
Das Pentagon-Datenleck ereignet sich während einer separaten Cybersicherheitsuntersuchung des FBI-Rekrutierungsportals FBIJobs.gov. Die Hackergruppe ShinyHunters beanspruchte die Verantwortung für diesen Vorfall und erklärte, sie habe auf Namen, Privatadressen, Telefonnummern, Sozialversicherungsnummern, Geburtsdaten und Notfallkontaktinformationen von FBI-Mitarbeitern zugegriffen.
In einer Erklärung gegenüber der New York Times und 404 Media am Montag erklärte ShinyHunters jedoch, dass sie die Daten nicht veröffentlichen werde, wie zuvor angedroht. Die Gruppe behauptete, der Vorfall sei „KEINE Erpressung, KEIN Lösegeld, NICHT finanziell motiviert” und beschrieb ihn als „eine Marketingkampagne zum Schutz unseres Geschäfts und zur aktiven Bekämpfung von Desinformation”.
Es wurde keine Verbindung zwischen dem FBI-Vorfall und dem Pentagon-Datenleck festgestellt.
—
DIE ANALYSE: EIN SYSTEMISCHES VERSAGEN DER NATIONALEN SICHERHEIT
1. Neun Monate unentdeckt ist ein katastrophales Versagen
Das Datenleck blieb etwa neun Monate unentdeckt. In Cybersicherheitsbegriffen ist das eine Ewigkeit. Die Erkennungsfähigkeiten des Pentagons versagten – nicht für Stunden oder Tage, sondern für den Großteil eines Jahres. Die Frage ist nicht, ob die Schwachstelle existierte – sondern warum neun Monate lang niemand sie bemerkte.
2. Die Daten waren nicht verschlüsselt
Die kompromittierten Datensätze waren nicht verschlüsselt. Dies ist ein grundlegendes Versagen der Datensicherheit. Die Verschlüsselung sensibler Personaldatensätze ist eine Grundvoraussetzung, kein optionales Upgrade. Das Versäumnis des Pentagons, diese Daten zu verschlüsseln – oder sicherzustellen, dass sie im Ruhezustand verschlüsselt waren – verwandelte eine Schwachstelle in eine Katastrophe.
3. Berufsfelder sind eine spionageabwehrliche Goldgrube
Die Offenlegung militärischer Berufsfelder ist besonders alarmierend. Jemand mit einem Namen, Kontaktinformationen und Berufsfeld könnte eine überzeugende Nachricht über die Zuweisung oder Leistungen einer Person erstellen oder Personal in Rollen von besonderem Interesse identifizieren. Ausländische Geheimdienste würden diese Daten als äußerst wertvoll für Targetierung und Rekrutierung erachten.
4. Das Pentagon hat keine Antworten
Das Pentagon hat die Angreifer nicht identifiziert, ihr Motiv nicht offengelegt, nicht festgestellt, wie viele Daten zugegriffen wurden, oder bestätigt, ob Daten kopiert wurden. Die Lücken im Wissen des Pentagons sind ebenso alarmierend wie das Datenleck selbst.
5. Sozialversicherungsnummern können nicht geändert werden
Anders als ein Passwort können eine Sozialversicherungsnummer oder ein Geburtsdatum nach einer Offenlegung nicht einfach geändert werden. Gestohlene Identitätsinformationen können mit öffentlichen Aufzeichnungen, kommerziellen Datenbanken, Social-Media-Profilen oder Informationen aus früheren Datenschutzverletzungen kombiniert werden, um überzeugende Social-Engineering- und Betrugsversuche zu erstellen. Die Konsequenzen dieses Datenlecks werden jahrzehntelang spürbar sein.
6. Das Timing ist verdächtig
Das Datenleck ereignete sich während einer Phase erhöhter US-Militäraktivität – einschließlich Angriffen gegen den Iran, der Seeblockade iranischer Häfen und des anhaltenden Krieges im Nahen Osten. Ob das Datenleck mit diesen Ereignissen zusammenhängt, ist unbekannt. Aber das Timing wirft Fragen auf, die Antworten erfordern.
7. Das FBI-Datenleck und das Pentagon-Datenleck sind nicht isoliert
Zwei große Datenschutzverletzungen von US-Regierungssystemen – das FBI-Jobportal und die Pentagon-Personaldatenbank – wurden innerhalb weniger Tage offengelegt. Ob sie miteinander verbunden sind oder nicht, sie offenbaren ein Muster: US-Regierungsbehörden versäumen es, die persönlichen Daten ihrer Mitarbeiter und ihres Personals zu schützen.
—
DAS FAZIT
Das Pentagon-Datenleck ist ein systemisches Versagen der nationalen Sicherheit:
1. 3 Millionen+ betroffen – 2,76 Millionen Lebende, 294.000 Verstorbene.
2. Neun Monate unentdeckt – Oktober 2025 bis Juli 2026.
3. Daten waren nicht verschlüsselt – ein grundlegendes Sicherheitsversagen.
4. Sozialversicherungsnummern offengelegt – können nicht geändert werden, Konsequenzen für Jahrzehnte.
5. Berufsfelder offengelegt – eine spionageabwehrliche Goldgrube.
6. Identität der Angreifer unbekannt – keine Antworten vom Pentagon.
7. Die Frage ist nicht, ob die Daten missbraucht werden – sondern wann.
Die Frage ist nicht länger, ob das Pentagon seine Personaldaten schützen kann – sondern ob ihm vertraut werden kann.
—
📁 EXKLUSIVES MATERIAL – PATREON
Alle exklusiven Materialfunde, vollständigen Dossiers und prädiktiven Geheimdienstbewertungen zum Pentagon-Datenleck, dem DMDC-System, dem FBI-Jobportal-Datenleck und dem breiteren Netzwerk von US-Regierungs-Cybersicherheitsversagen sind nur unter patreon.com/berndpulch verfügbar.
Exklusiv für Abonnenten verfügbar:
· Vollständige Datenleckanalyse – Komplette Zeitleiste, Datenkategorien, Aufschlüsselung der betroffenen Bevölkerung
· DMDC-System-Dossier – Systemarchitektur, Sicherheitskontrollen, Schwachstellen
· Angreifer-Tracker – Bekannte und vermutete Akteure, Zuschreibungsbewertungen, Motivanalyse
· FBI-Datenleck-Datenbank – ShinyHunters-Behauptungen, FBI-Reaktion, Datenveröffentlichungsstatus
· Prädiktive Geheimdienste – Bewertungen von Datenmissbrauch, Identitätsdiebstahl-Auswirkungen und Kongressreaktion
Unterstützen Sie unabhängige Geheimdienstarbeit. Greifen Sie auf das Rohmaterial zu. Nur unter patreon.com/berndpulch.
—
© INTELLIGENCEORIGINAL.COM – ABOVE TOP SECRET ORIGINAL DOKUMENTE – DAS EINZIGE MEDIUM MIT LIZENZ ZUM SPIONIEREN
—
📢 TEILEN SIE DIESE INFORMATIONEN
📺 YouTube: youtube.com/@bernd_pulch
🐦 X (Twitter): x.com/berndsocial1
📢 Telegram: t.me/ABOVETOPSECRETXXL
🔓 Enthülle die ganze Wahrheit: berndpulch.org/join
—
🔓 Unterstützen Sie unabhängige Geheimdienstarbeit — Monero (XMR):
45cVWS8EGkyJvTJ4orZBPnF4cLthRs5xk45jND8pDJcq2mXp9JvAte2Cvdi72aPHtLQt3CEMKgiWDHVFUP9WzCqMBZZ57y4
https://api.qrserver.com/v1/create-qr-code/?data=45cVWS8EGkyJvTJ4orZBPnF4cLthRs5xk45jND8pDJcq2mXp9JvAte2Cvdi72aPHtLQt3CEMKgiWDHVFUP9WzCqMBZZ57y4&size=150×150
—
WARUM IHRE UNTERSTÜTZUNG WICHTIG IST
Unabhängige Geheimdienstarbeit ist nicht kostenlos. Im Gegensatz zu den Unternehmensmedien akzeptieren wir keine staatliche Finanzierung, keine Werbung und keine institutionelle Unterstützung. Unsere einzige Währung ist Ihr Vertrauen – und Ihre Unterstützung.
Ihre Spende ermöglicht es uns:
1. Vollständige Unabhängigkeit zu wahren – Keine Werbetreibenden, keine Sponsoren, keine Paywalls.
2. Investigative Arbeit fortzusetzen – Anwaltskosten und Dokumentenbeschaffung kosten Geld.
3. Die Privatsphäre der Leser zu schützen – Wir verwenden verschlüsselte Kommunikation, sichere Infrastruktur und Monero.
4. Unsere Reichweite zu erweitern – Jede Spende hilft uns, mehr Analysten und Bürger zu erreichen.
5. Unkompromittiert zu bleiben – Wir veröffentlichen, was andere nicht tun.
6. Unser unabhängiges internationales Netzwerk zu erhalten – Sichere Server und globale Quellen erfordern ständige Investitionen.
7. Der Lawfare zu widerstehen – Rechtliche Herausforderungen und Drohungen sind kostspielig.
Nur Monero. Keine Spur. Kein Kompromiss.
—
Teilen Sie diese Informationen – die Wahrheit muss ans Licht kommen.
Leave a Reply